Custodia One / Compliance
Compliance.
Making compliance practical, operational and sustainable.
Custodia One supports organisations across Audit, Advisory, Implementation and Training for global standards and compliance frameworks. We help assess readiness, close gaps, implement controls and build the internal capability required to sustain compliance.
01 / Our Services
A clear path from readiness to resilience.
Compliance work should translate into better operating practice. Our services are structured to meet organisations where they are and move them toward a capability that can be sustained internally.
AUDIT
Readiness assessments, gap analysis and audits against applicable standards.
ADVISORY
Practical guidance, compliance roadmaps and specialist support.
IMPLEMENTATION
Translating requirements into policies, processes, controls and operating practices.
TRAINING
Building internal knowledge and capability for effective, ongoing compliance.
02 / Specialist Expertise
Experience that holds up in practice.
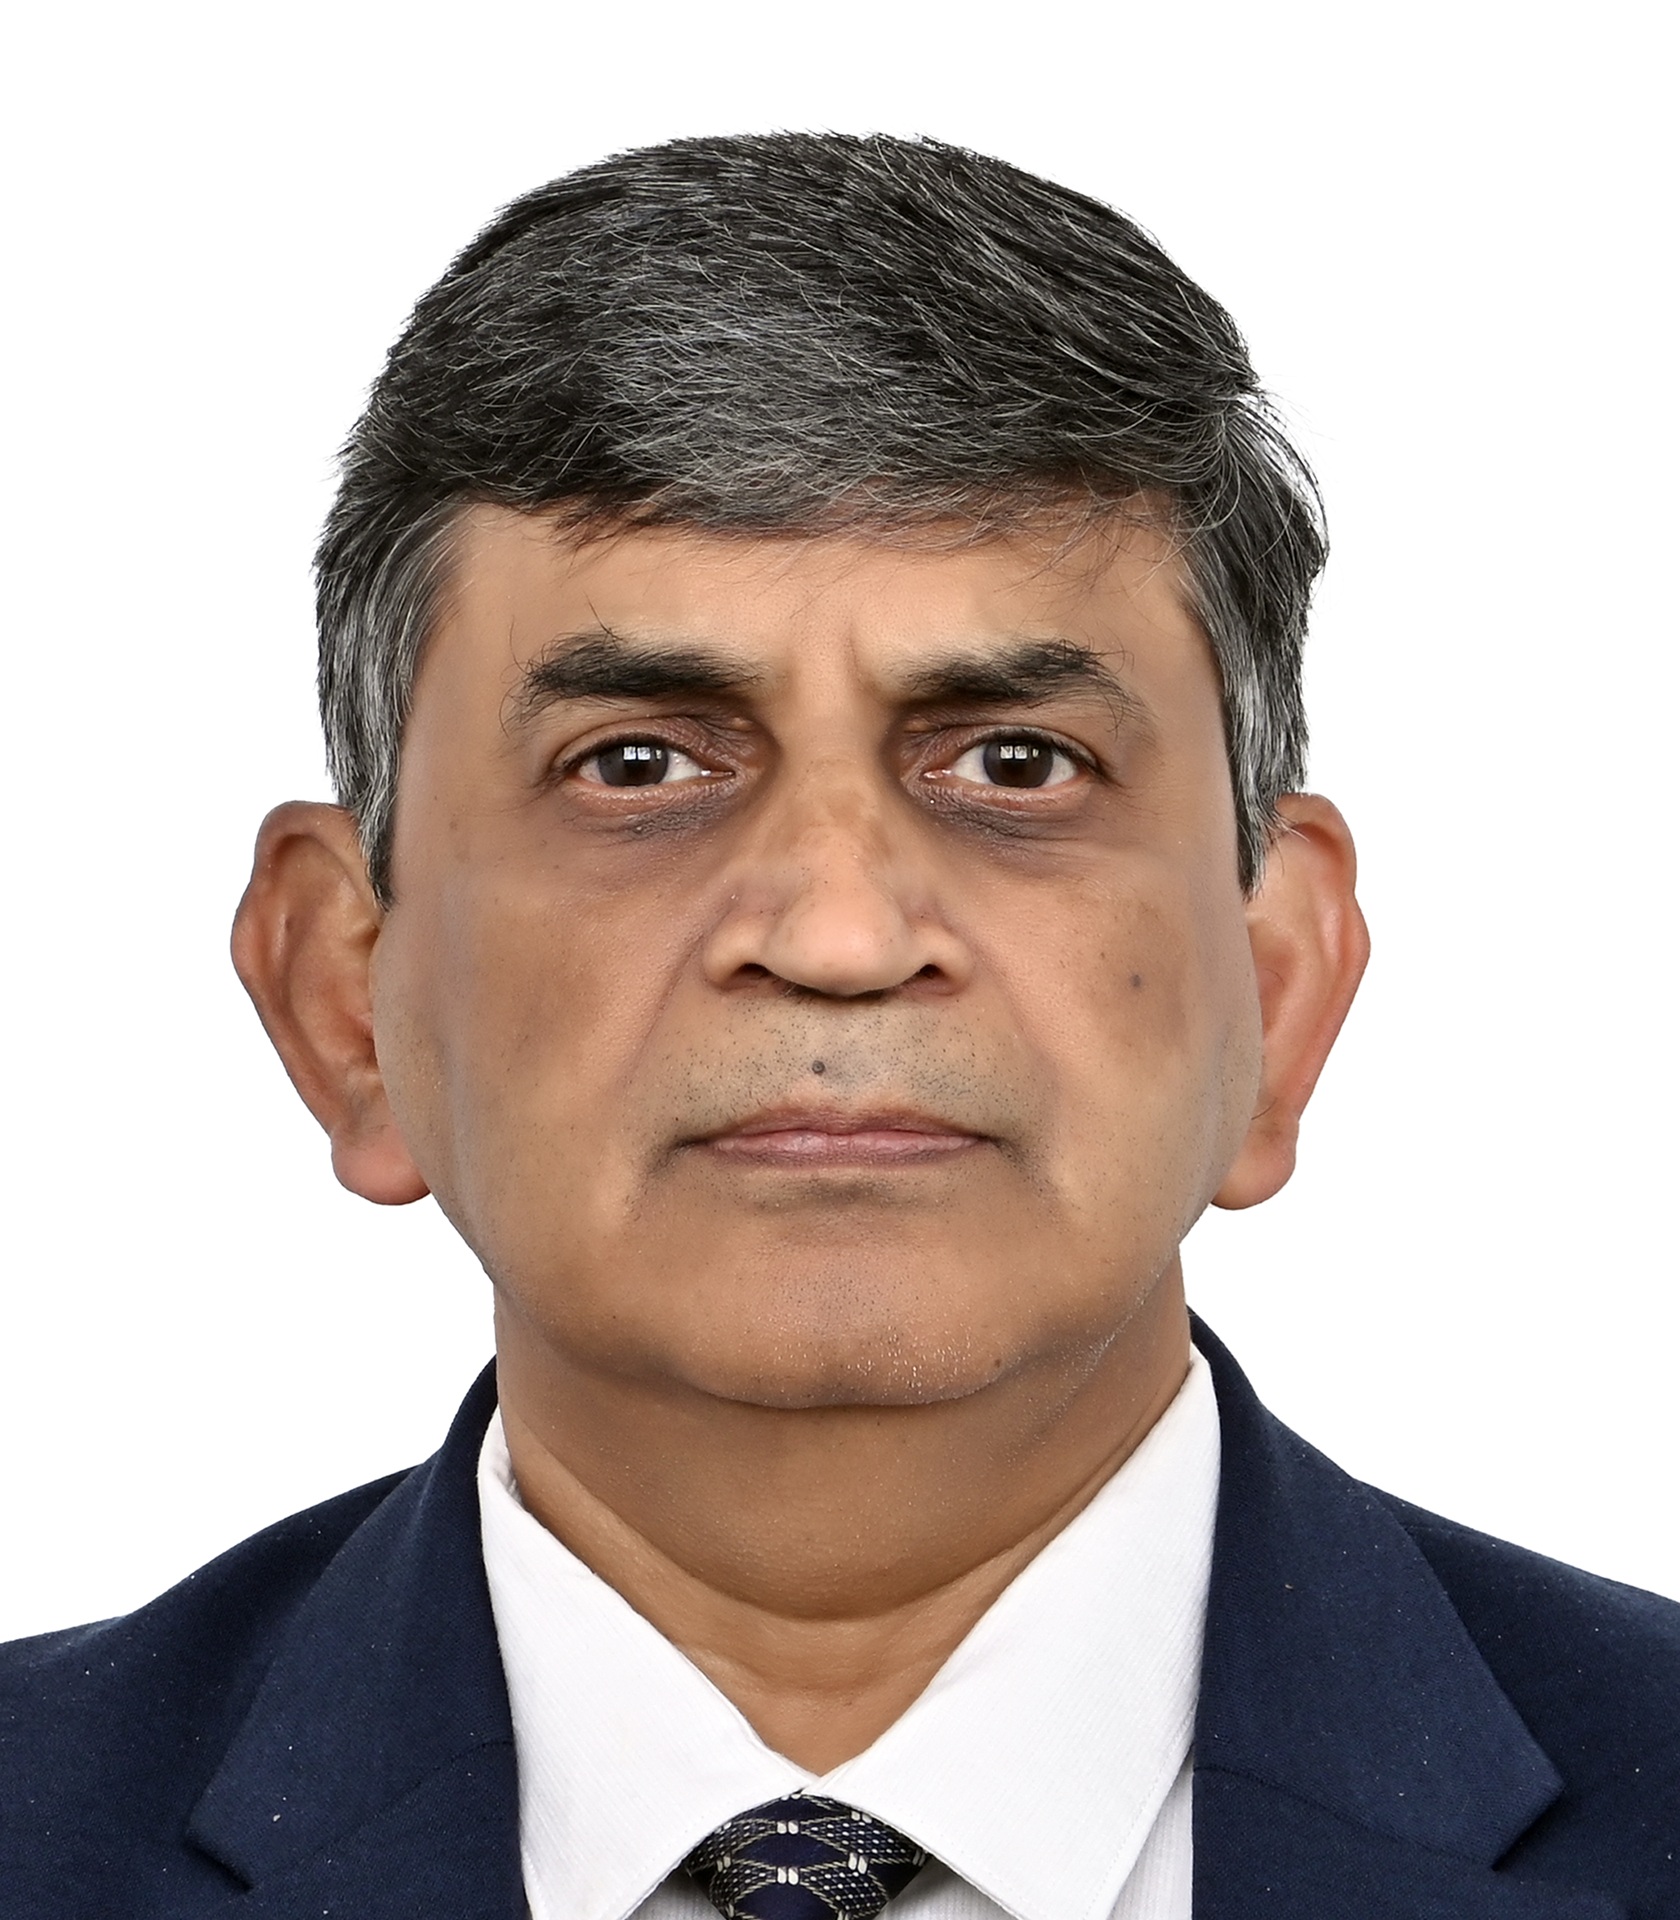
Muktesh Murthy brings over three decades of experience across compliance, audits, implementation, training, IT transformation and programme management. He has been auditing for over 25 years across ISO, CMMI, GDPR and PCI-DSS, with more than 2,000 days of internal audit experience and over 400 days conducting external audits in 25 countries worldwide.
His implementation experience includes 15+ end-to-end standards implementations across ISO, CMMI, GDPR, NIST and other frameworks. He has also delivered professional training for more than 25 years across ISO standards, programme and project management, information security, data privacy, business continuity and organisational capability building.
A certified lead auditor, trainer, consultant and programme management specialist, his international work spans multiple markets and sectors, bringing both technical depth and practical implementation experience to Custodia One's compliance engagements.
03 / Standards & Frameworks
The standards that shape the work.
ISO/IEC 27001
Information security
ISO/IEC 27701
Privacy Management
ISO/IEC 42001
AI management
ISO 9001
Quality
ISO/IEC 20000-1
IT service management
ISO 22301
Business continuity
ISO 14001
Environment Management
ISO 45001
Occupational Health and safety
CMMI Dev, Services, Testing
Software maturity (Level 3 to 5)
GDPR, DPDA
Data protection regulations
SAP GRC
Governance, risk, controls
SOC 1
Service organisation controls
SOC 2
Security, availability, privacy
Project Mgmt.
PMP / PRINCE2 / PRINCE2Agile practice
NIST
CSF, 800-53
ISO 31000
Risk Management
Compliance engagements